Navigate the Privileges menu
Navigate the Privileges menu

This is for:
System AdministratorIf you have permission to create or edit member groups, you can access the Privileges menu to manage the privileges granted to a member group.
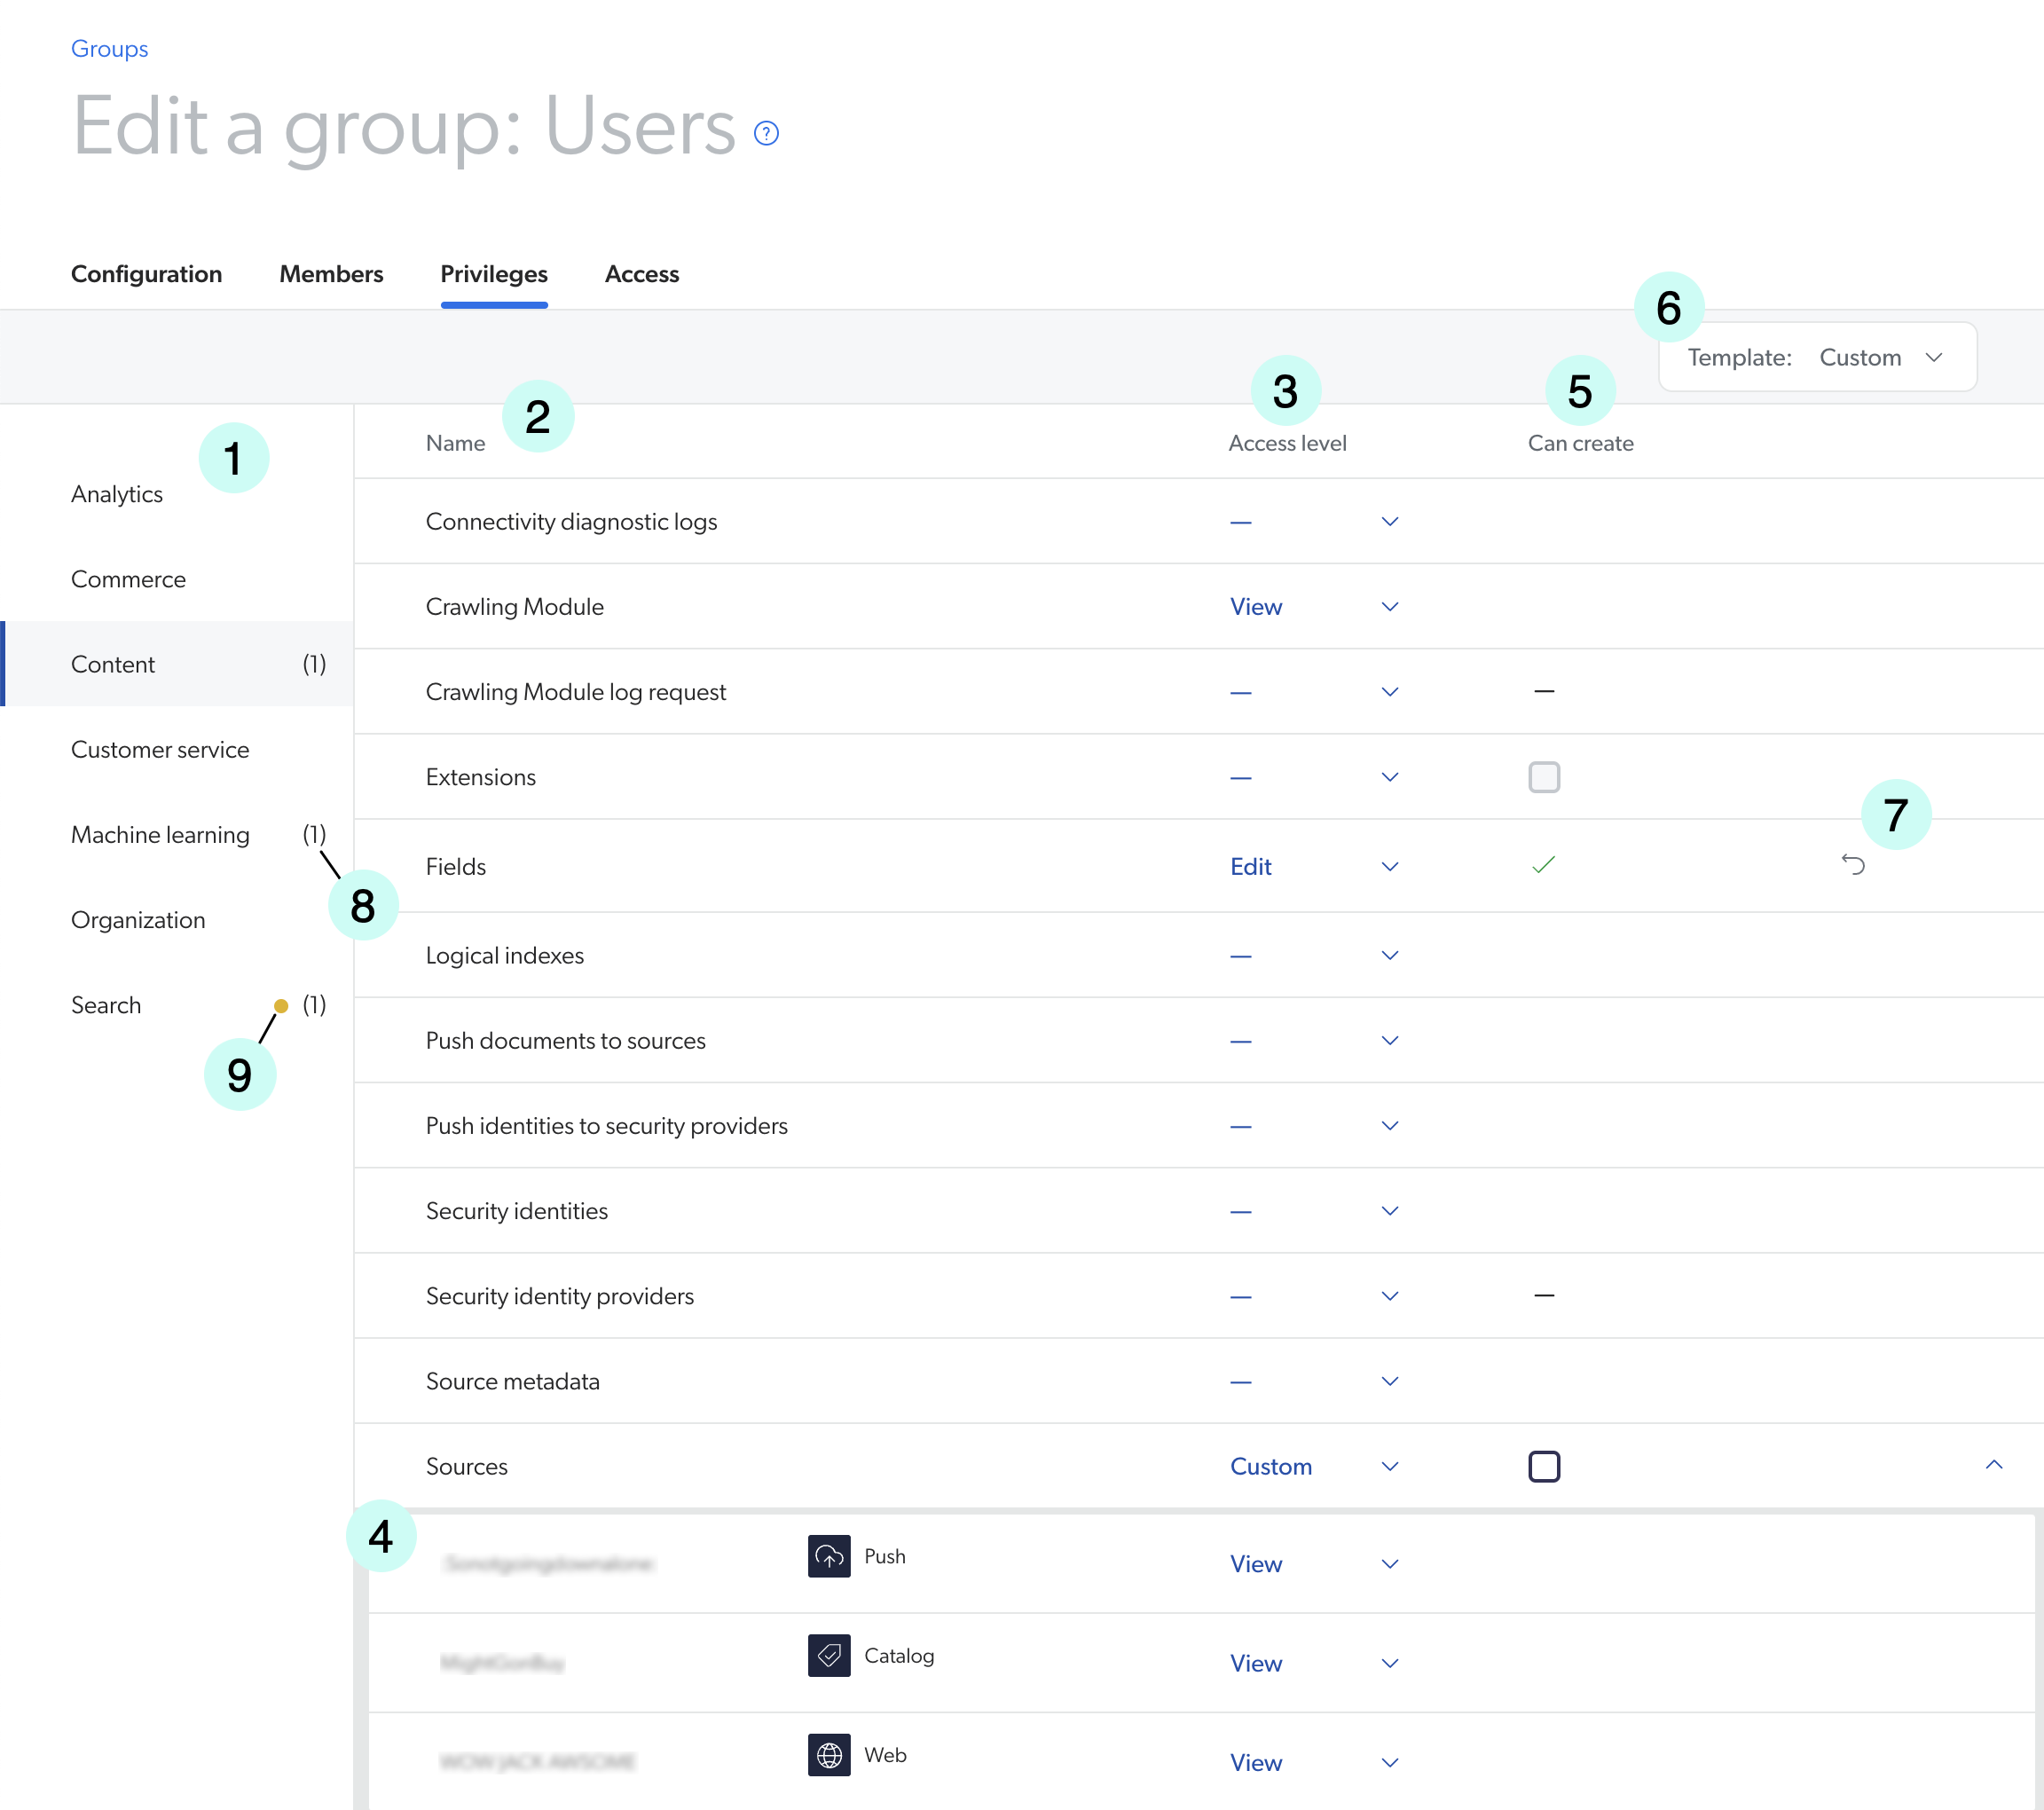
1 |
List of services |
2 |
List of domains |
3 |
Access Level column |
4 |
List of resources |
5 |
Can create ability |
6 |
|
7 |
Discard changes button |
8 |
Unsaved changes indicator |
9 |
Warning indicator |

|
Notes
|
Example
The following example shows the potential effects of varying access levels on the Coveo Administration Console. The access levels assigned to a member group are as follows:
-
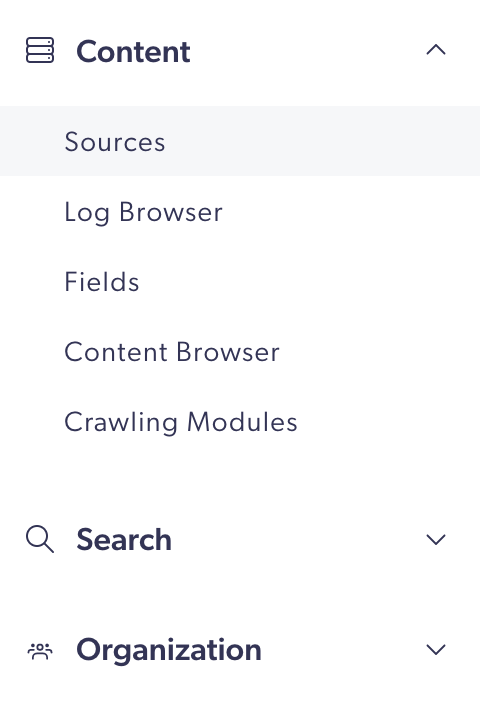
The Extensions domain isn’t assigned any access level.
-
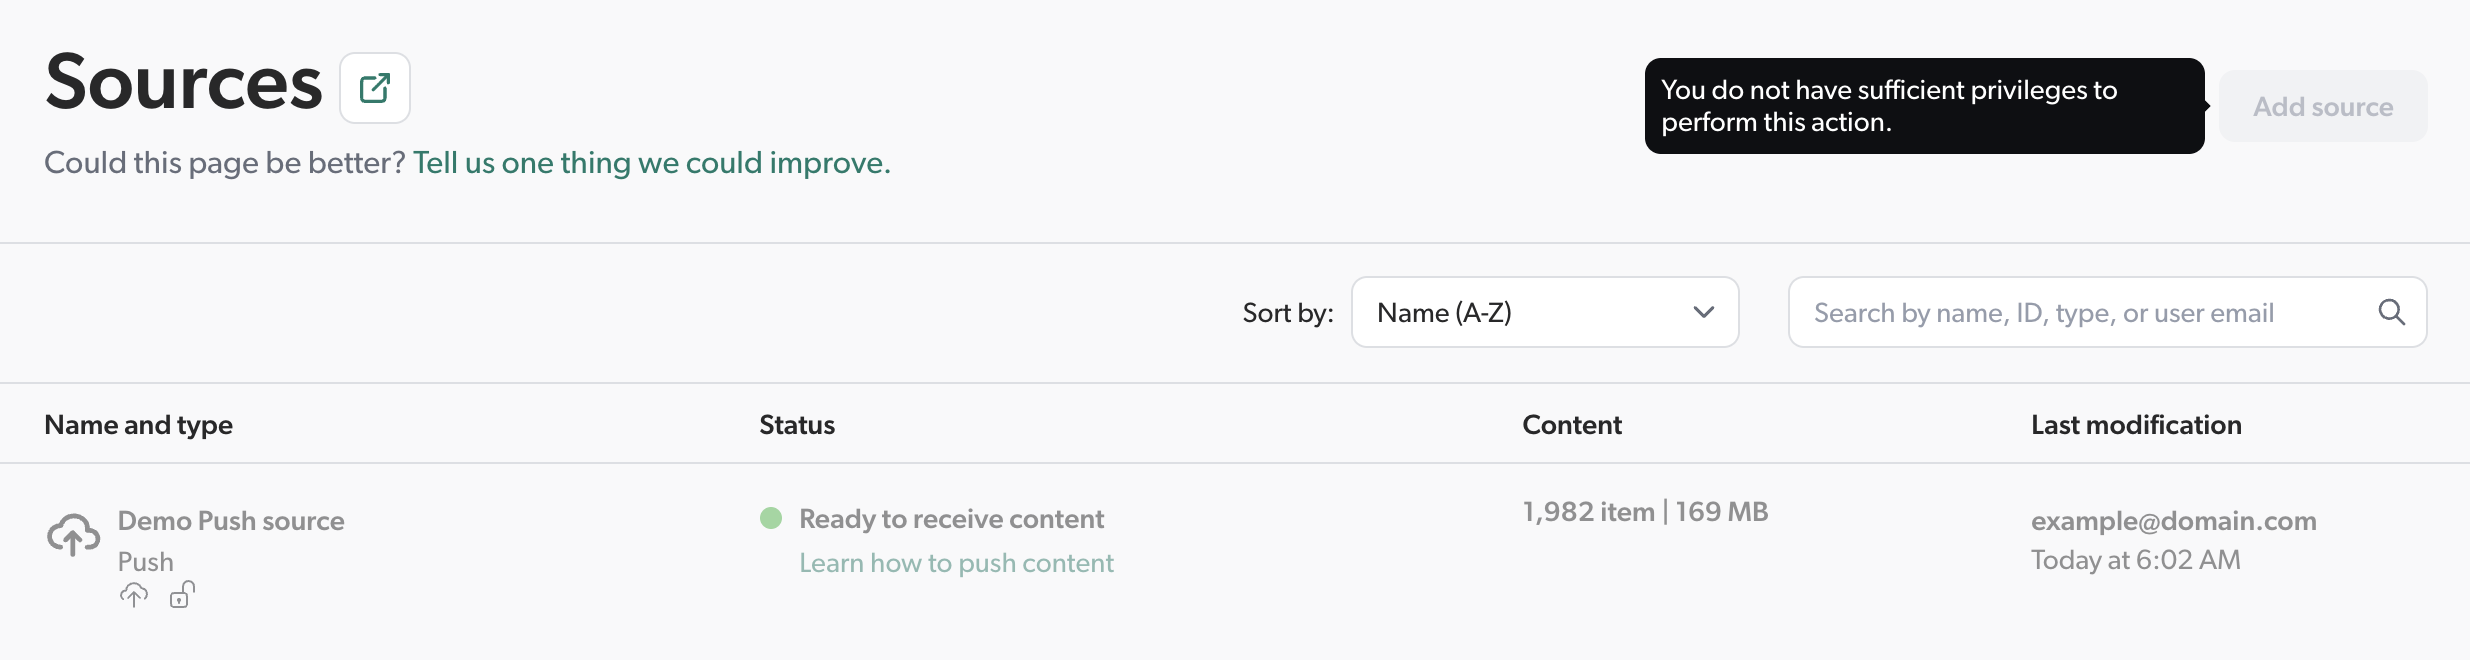
The Sources domain is set to View all.
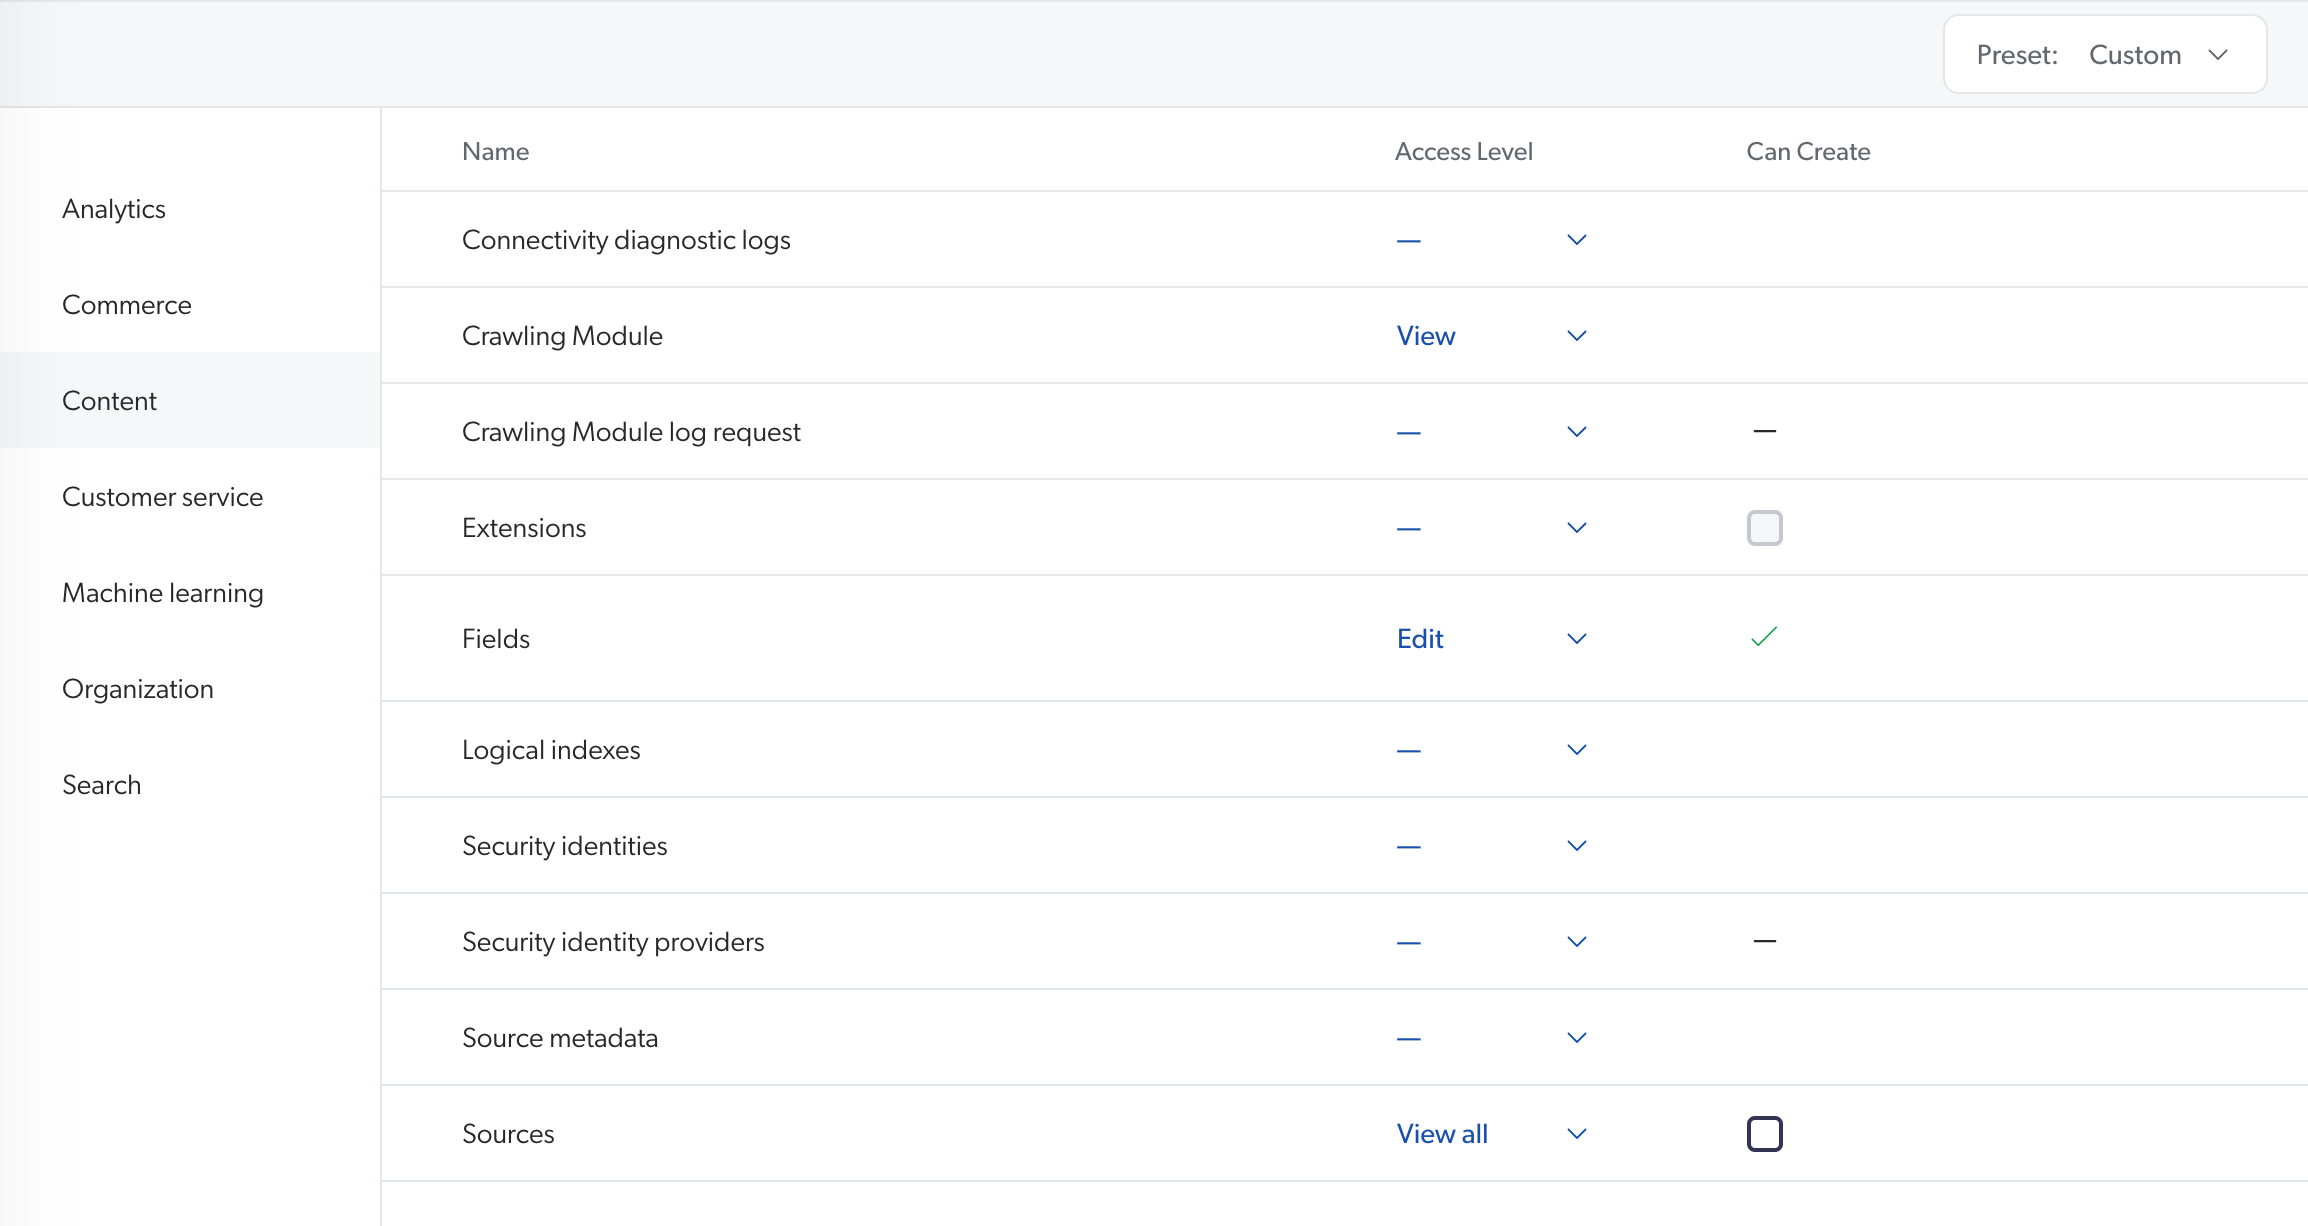
As a result, the Extensions page isn’t visible in the navigation menu for a member of this group.
On the Sources page, members can review source configurations but not edit them. Additionally, the Add source button is grayed out and unresponsive. When a member hovers over this button, a tooltip appears indicating that the member has insufficient privileges for adding a new source.
About privilege templates
When creating a group, you’re prompted to select a privilege template, that is, a pre-built set of privileges. Most privilege templates are based on a role and allow a certain type of Coveo Administration Console user to fulfill their duties. For example, the Analytics Manager template allows users to edit data exports, dimensions, reports, and other resources to manage their organization’s analytics. Alternatively, you can use one of the base templates to quickly grant a basic set of privileges, like full access or view-only access.
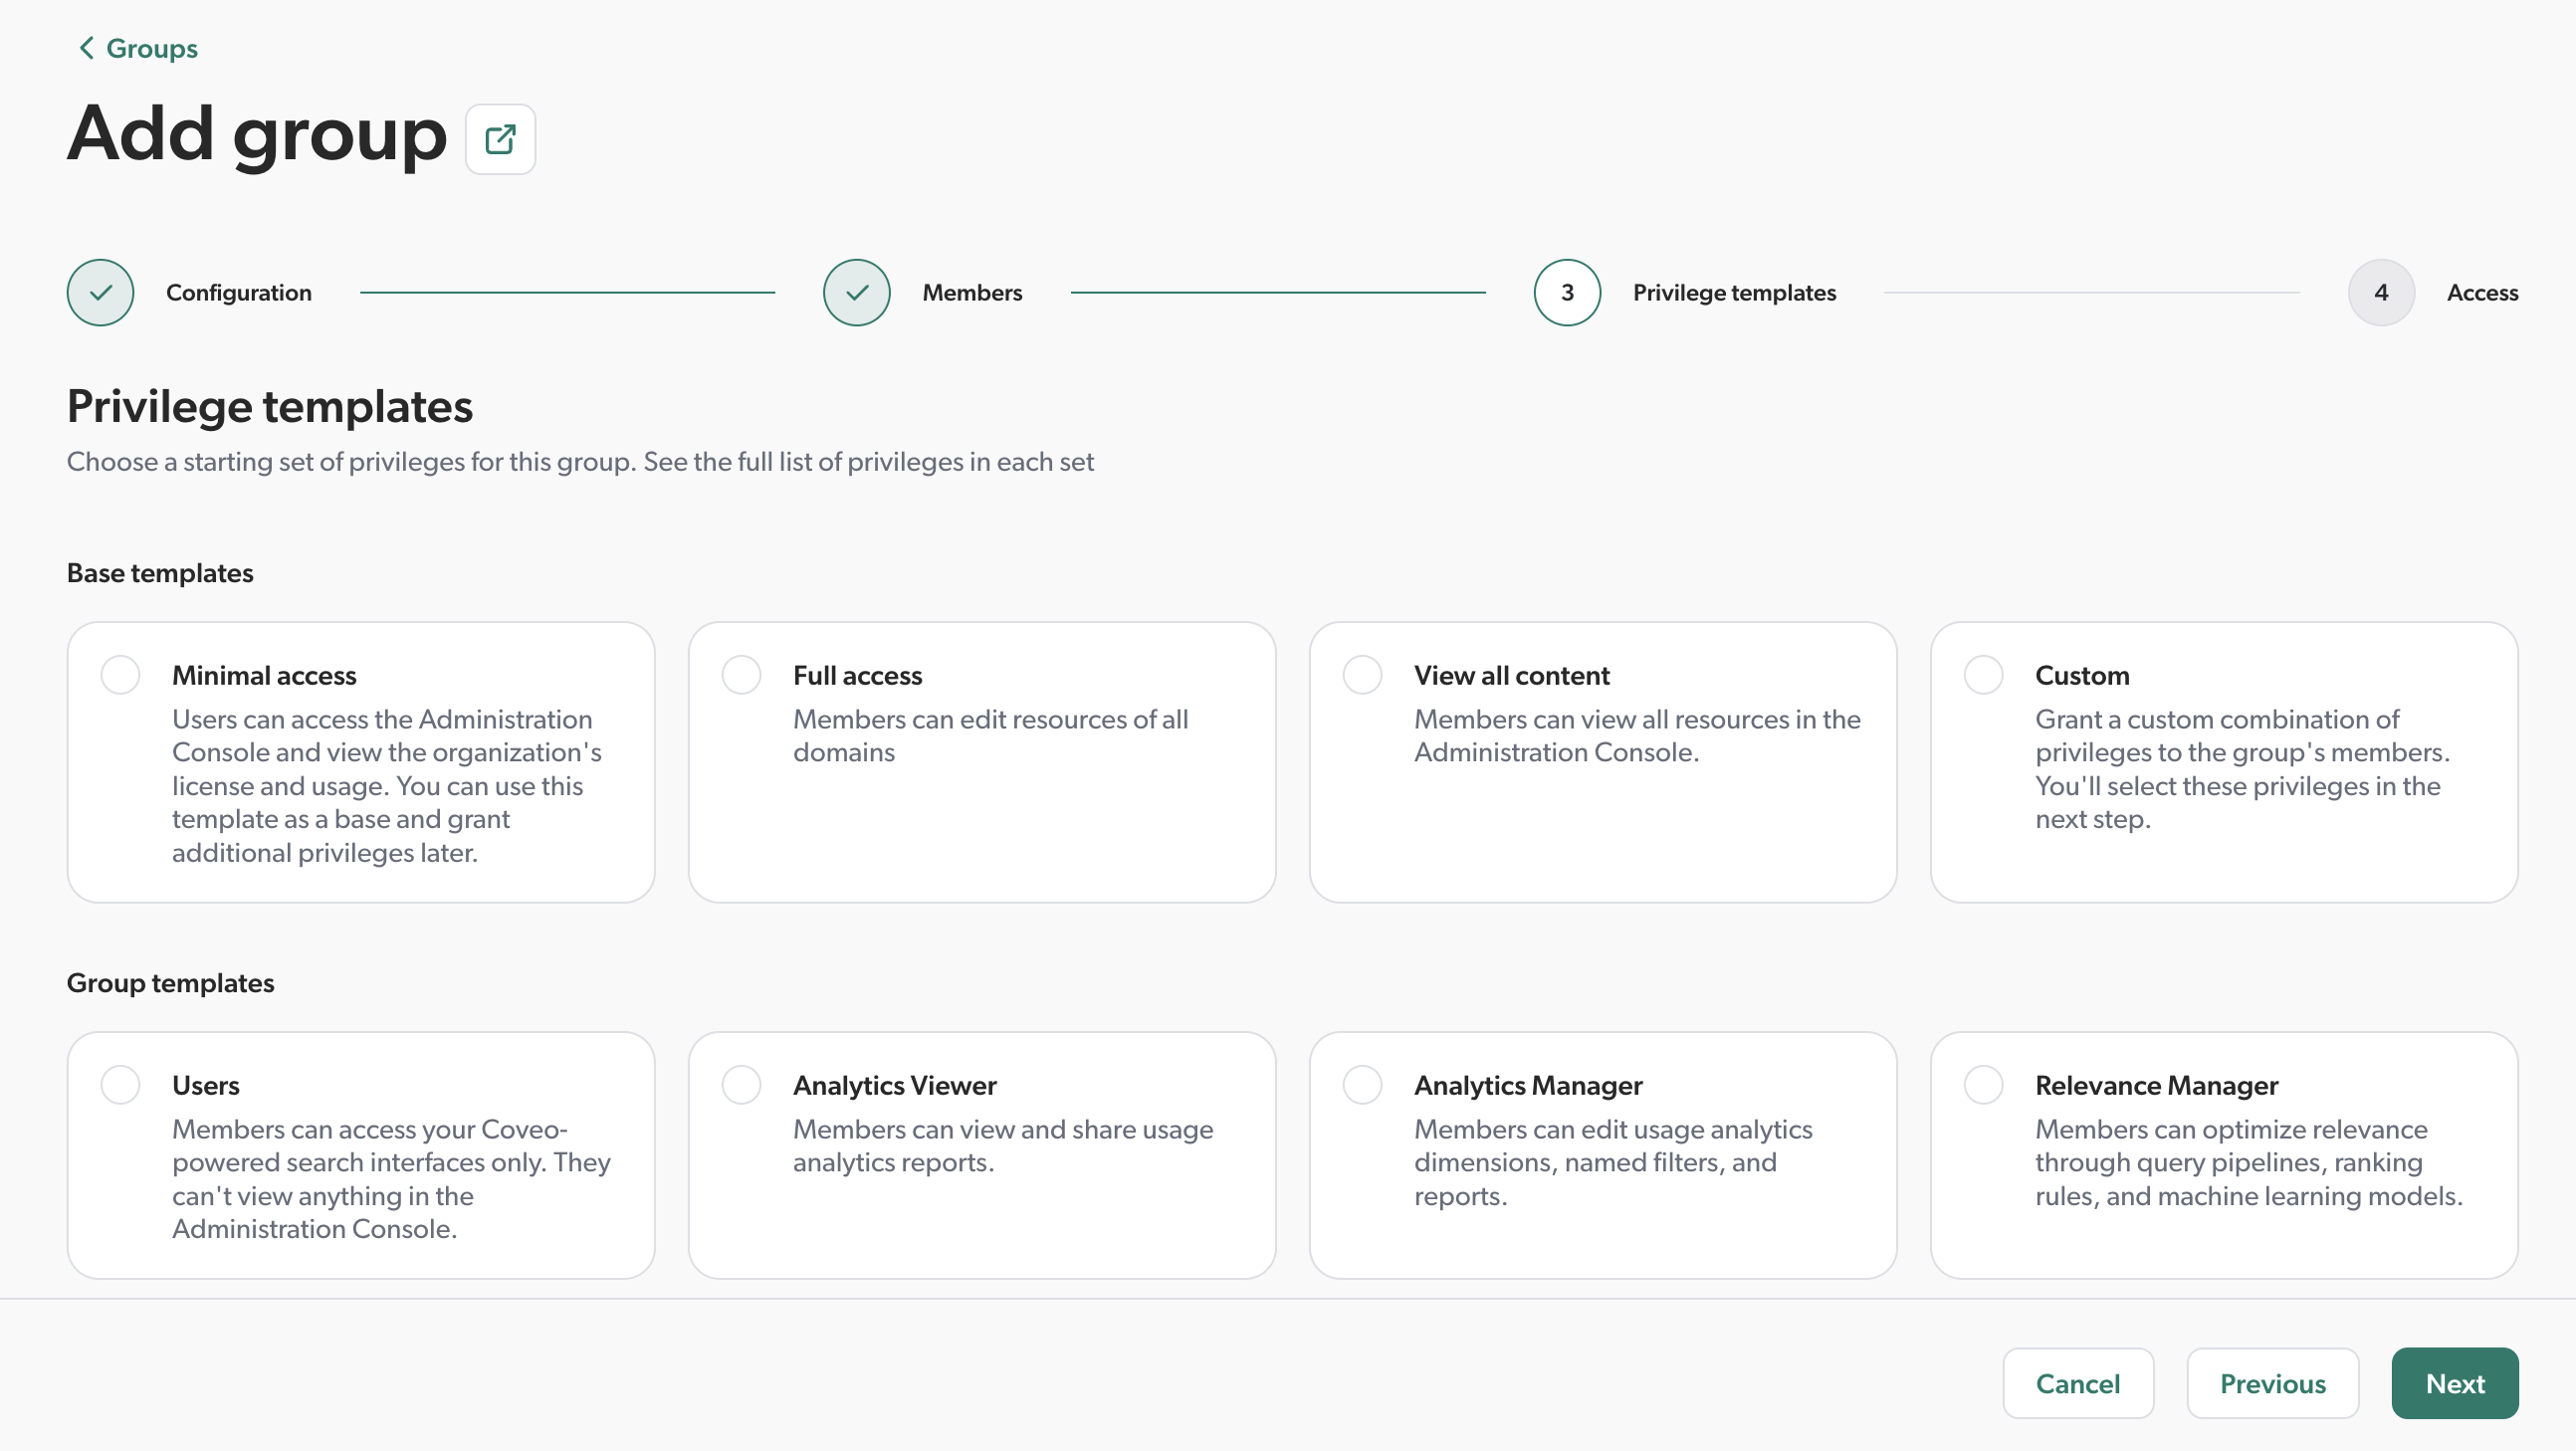
Similarly, when editing a group, you can either use a pre-built set of privileges, or start from a set and edit individual privileges as needed.
You can always edit the privileges granted to a group through a certain set.
In other words, you can save time by selecting the template closest to the privilege set you want to grant, and then editing the group and its privileges.
For example, if you want the members of a group to be able to edit sources and fields only, you can select the Minimal access template, which only grants the privilege to access the Coveo Administration Console, and then edit the group’s privileges to switch to the Edit access level for the Sources and Fields domains.
The Template dropdown menu then indicates: Custom set of privileges.
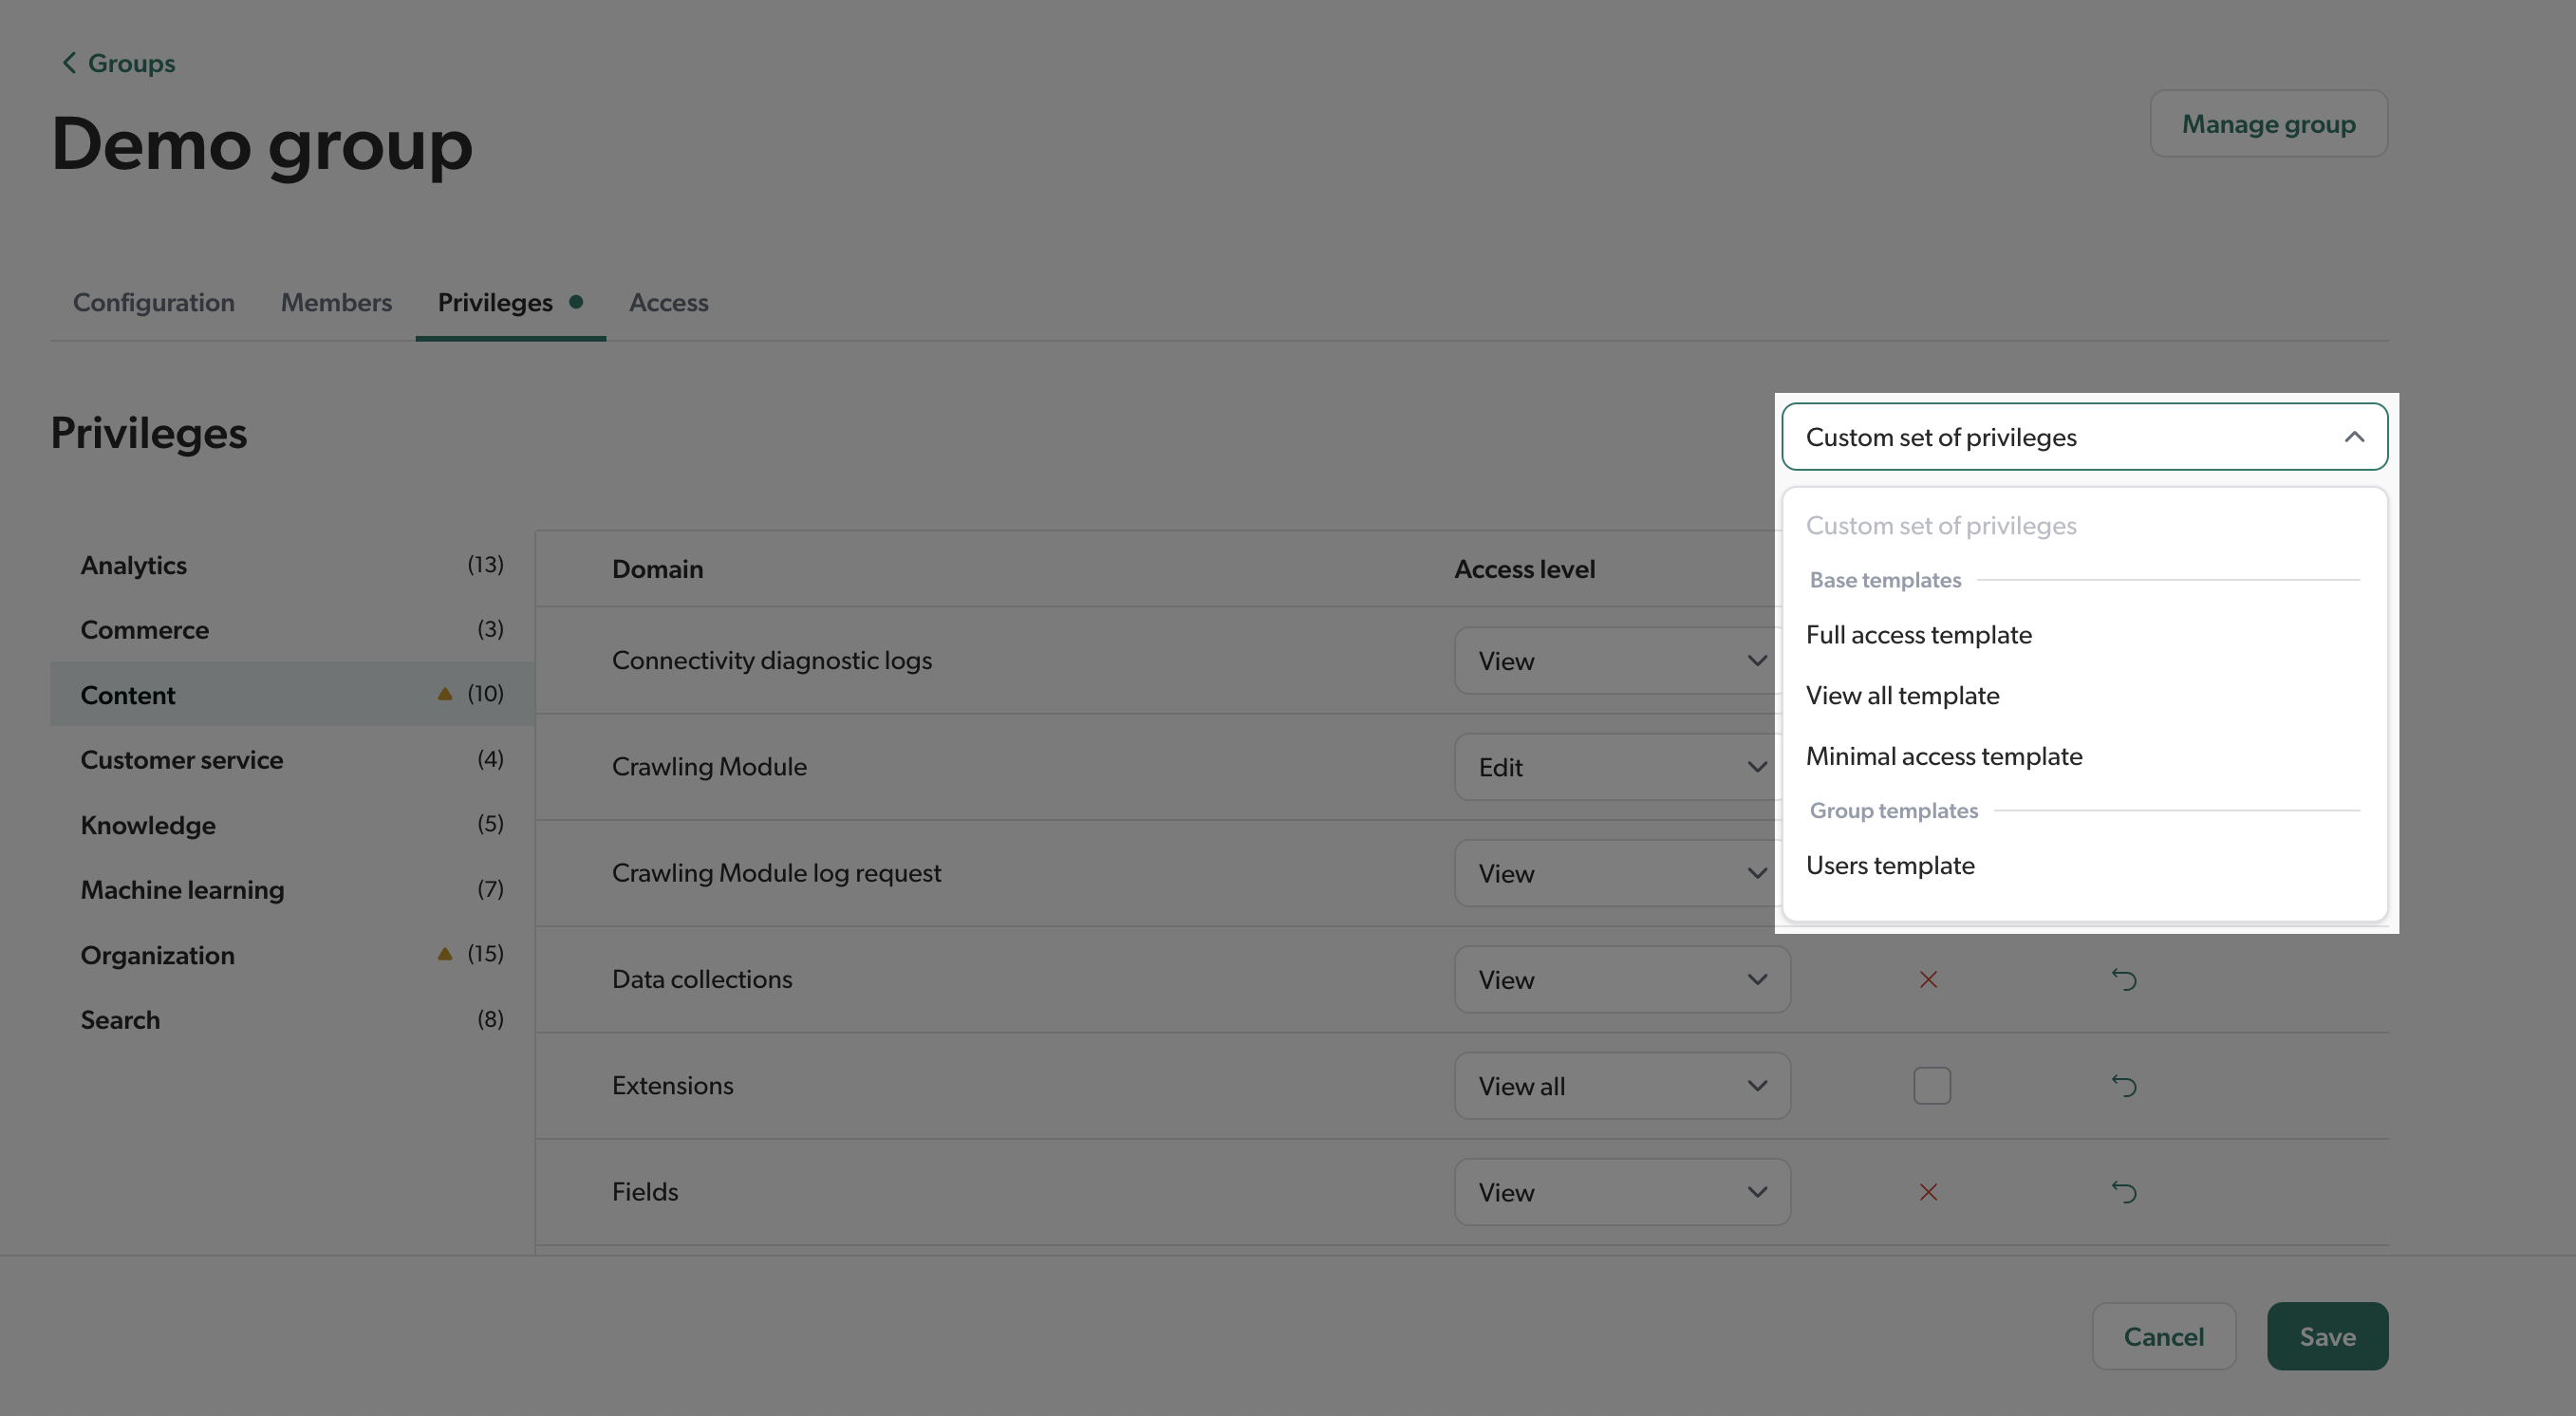
For details on each privilege template, see Built-in groups. The role-based templates are based on the built-in groups offered on the Groups (platform-ca | platform-eu | platform-au) page. See also the privilege reference page for a detailed list of the privileges in each template.
|
|
Note
If you don’t have all the privileges in the template you select, the missing privileges can’t be applied to the group. To fully apply a template, you must have the same or a higher access level for each domain, as the access levels you can grant depend on your own the access level. For example, if you have the privilege to view all sources, you can’t grant the Edit all or Custom access levels on the Sources domain to a group. Your only options are View all and No access. |
What’s next?
Learn about granting privileges.