About the login process
About the login process

This is for:
System AdministratorUsers must log in to access the Coveo Administration Console, the Coveo Merchandising Hub, the Knowledge Hub, and other resources such as Coveo Connect. Some Coveo-powered search interfaces also require users to log in, especially if the search results they return are sensitive.
This page explains the login process that users must follow once their Coveo administrator invites them to join an organization It provides an overview of the available login options, procedures for tasks such as switching identity providers, and troubleshooting guidance for common login errors.
Invitation email
When you add a member to a Coveo organization, they receive an invitation email. They must click the link in the email to log in and accept the invitation. This link expires after 31 days.

Login options
 Coveo relies on third-party identity providers to authenticate members.
Coveo requires that its members to log in using an account with one of the following identity providers:
-
Google
-
Microsoft
-
Salesforce
-
Another single sign-on (SSO) identity provider
When clicking either Google, Microsoft, or Salesforce, members are prompted to enter their credentials. For example, here’s Google’s prompt:

Logging in with a custom SSO
 If you implemented a SAML SSO other than Google, Microsoft, or Salesforce, you must instruct members to click Log in with a custom SSO on the login page, and then enter the ID of the organization they want to access.
You should also provide this ID to new members when adding them to your Coveo organization, but if you haven’t, a link allows them to get a list of the organizations they can log in to.
After a member’s first login, Coveo stores the organization ID in a cookie and automatically fills the Organization ID box next time.
Logging in with email
 The email option allows members to log in without an account with one of the supported identity providers.
It’s mostly used by new members of Coveo, especially those starting a free trial.
The login flow is the following:
-
On the login page, the member clicks Log in with email.
-
The member provides their email address.
-
Coveo sends them an email with a login link.
-
When the member clicks this link, the Coveo Administration Console opens in a new browser tab. They’re automatically logged in.
-
The next time the member needs to log in to Coveo, they repeat steps 1 to 4 with the same email address.

|
Leading practice
While convenient for getting started, email login isn’t the best long-term option. If ready to commit to a full Coveo license, you should switch to an SSO provider such as Google, Microsoft, Salesforce, or a custom SSO. SSO offers a faster, smoother, and more secure sign-in experience, and it scales better as your organization grows. See Benefits of switching to SSO for details. |
Coveo administrators can also use email login as a "backdoor" for their single sign-on implementation.
Benefits of switching to SSO
If ready to commit to a full Coveo license, you should switch to using Google, Microsoft, Salesforce, or another SSO provider for a better experience in the long term. For example, if your company uses Okta for SSO, you should implement it in your Coveo organization and have all Coveo users log in with this option. The advantages of this change are the following:
-
Logging in becomes faster and smoother. If members are already logged in to the SSO on another web application, they don’t have to enter their password and are automatically let in. They don’t have to switch to their inbox and wait for Coveo’s email.
-
Relying on a single system to manage user access reduces the risk of unauthorized access. For example, if an employee logs in to Coveo with their personal email, they can still access Coveo after leaving your company if you don’t manually delete their identity in the Coveo Administration Console. However, if they access Coveo with a company-managed account, this account is typically deactivated as part of the employee offboarding process.
After login
After their first login as a member of the group they have been added to, the member must accept the invitation to join this group. They’re then redirected to the Coveo application or search page they wanted to access.

Moreover, if it’s the first time they’re logging in with these credentials, members receive an email asking to confirm their email address.
Switching to a different provider
Switching from an identity provider to a different identity provider is essentially adding a new organization member, and then removing the original one. This must be done even if the user receives Coveo login links to their Google, Microsoft, or Salesforce address.
-
Add the user as a new member of your Coveo organization, selecting the new identity provider. Make sure to add them to the same groups as their original account to preserve their privilege set.
Multiple accounts
You can add the same person to your organization more than once, either by using different identity providers, such as Google and Microsoft, or by using email aliases, like jsmith@domain.com and john.smith@domain.com.
Coveo considers the two sets of credentials to be independent and can’t tell if they represent the same individual.
As a result, these two accounts can be granted different privileges.
After you add a member to your organization, make sure they log in using the same identity provider and exact email address that you used to invite them.
Login page address
The URL of the login page can differ depending on the region and whether your Coveo deployment is HIPAA-compliant.
| Region | Login page URL |
|---|---|
US |
|
US (HIPAA-compliant) |
|
Canada |
|
Ireland |
|
Australia |
Alternatively, you can use the following addresses and replace <ORG_ID> with the unique identifier of your Coveo organization:
-
<ORG_ID>.admin.org.coveo.com -
<ORG_ID>.admin.orghipaa.coveo.comfor HIPAA organizations
Coveo will redirect you based on your primary deployment region, as listed previously.
Troubleshooting
When trying to log in, members might encounter the following messages:
"You currently don’t have access to any organizations"

|
Context and symptoms
When trying to log in, the member sees the following message:
The member’s credentials are valid, but don’t match any Coveo organization member. Likely cause and resolutionCause This message can have one of the following causes:
Resolution Depending on the cause, try the following:
|
"Insufficient privileges"
|
|
Context and symptoms
When trying to log in, the member sees the following message:
Likely cause and resolutionCause The member tried to log in to an organization that they don’t have the privilege to view. Resolution Grant the member the privilege to view the organization (View access level on the Organization domain). |
"AADSTS90093: Does not have access to consent" or "Need admin approval"
|
|
Context and symptoms
When trying to log in, the member sees one of the following messages:
Likely cause and resolutionCause A Microsoft Office 365 global administrator disabled the ability for users to consent to third-party applications such as Coveo. Resolution An Office 365 global administrator can either:
The process of having an Office 365 global administrator give consent to Coveo is the following:
Contact the Coveo Support team if the error persists. |
"Salesforce OAuth Error"
|
|
Context and symptoms
When trying to log in, the member sees the following message:
For example: 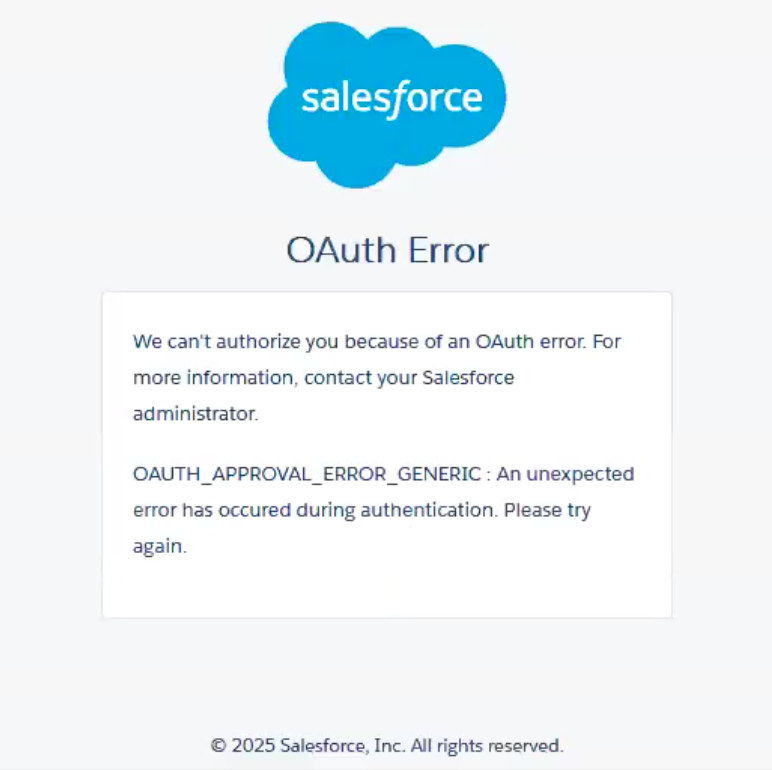
The URL of the error page ends with Likely cause and resolutionCause The Coveo Connected Apps haven’t been installed in the user’s Salesforce organization. Resolution
|