---
title: Configure Okta for Coveo SSO
slug: '1602'
canonical_url: https://docs.coveo.com/en/1602/
collection: manage-an-organization
source_format: adoc
---
# Configure Okta for Coveo SSO
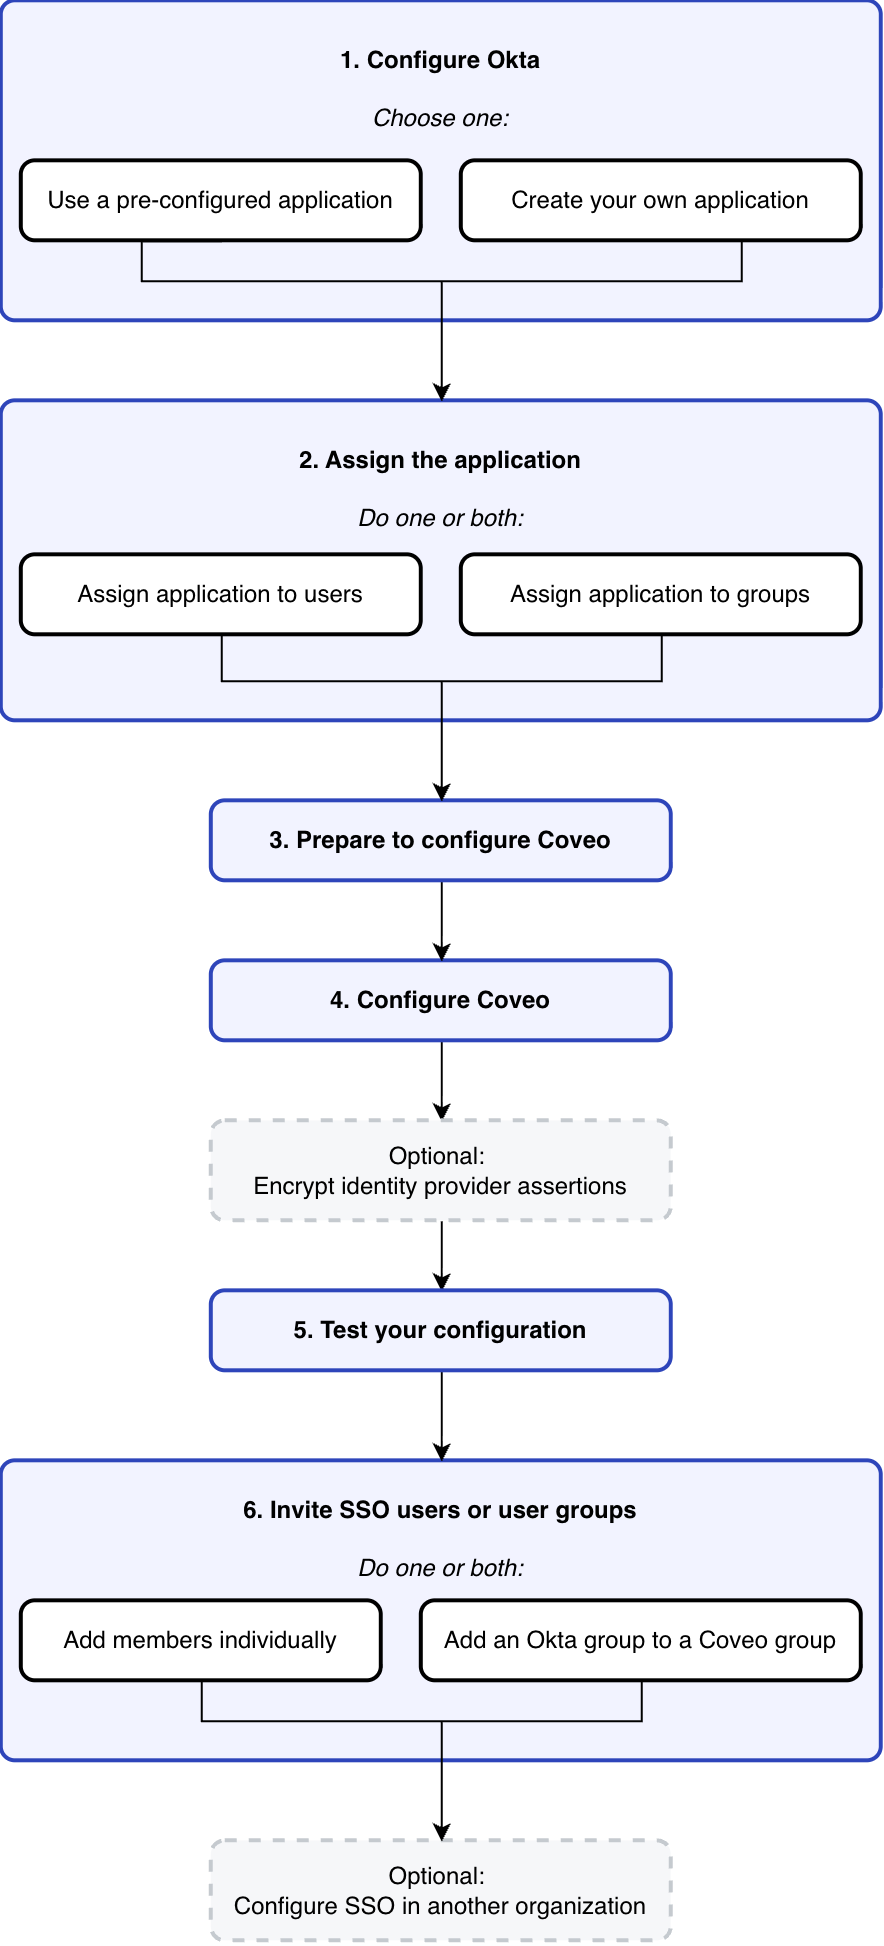
![Okta SSO configuration flowchart](https://docs.coveo.com/en/assets/images/manage-an-organization/sso-okta-flowchart.png)

[Okta](https://www.okta.com/products/single-sign-on/) is a service providing single sign-on (SSO) for web and mobile applications.

As a Coveo administrator, you can [implement Security Assertion Markup Language (SAML) 2.0 SSO](https://docs.coveo.com/en/1979.md) when your company uses Okta.
Users can then log in to Coveo without having to provide their authentication credentials since their identity has previously been validated when logging in to their Okta session.

To allow users to log in via SAML SSO, Coveo must be able to trust and rely on Okta to authenticate users wanting to log in.
To establish this trust relationship, you must configure Okta and Coveo so that both parties can exchange authentication information.
This page explains how to proceed.

To configure SSO in more than one Coveo organization, for example in a production organization and a [sandbox organization](https://docs.coveo.com/en/2959.md), configure one of these organizations, and then follow [the instructions](#configure-sso-in-another-organization) at the end of this page.

> **Note**
>
> If you're not the Okta administrator at your company, contact them so that they configure Okta using the following steps.
> Provide them with the Coveo public certificate, which is needed to [encrypt assertions](#encrypt-okta-assertions).
> You can find this certificate on the **Settings** page of the [Coveo Administration Console](https://docs.coveo.com/en/183.md), under **Organization** > [**Single sign-on**](https://platform.cloud.coveo.com/admin/#/orgid/settings/organization/sso) ([platform-ca](https://platform-ca.cloud.coveo.com/admin/#/orgid/settings/organization/sso) | [platform-eu](https://platform-eu.cloud.coveo.com/admin/#/orgid/settings/organization/sso) | [platform-au](https://platform-au.cloud.coveo.com/admin/#/orgid/settings/organization/sso)).

## Configure Okta

Both Okta and Coveo must be configured to work together and provide a SAML SSO service to your Coveo users.
First configure Okta so that it can provide Coveo with user authentication data.

1. Log in to your [Okta Developer](https://developer.okta.com/) account.

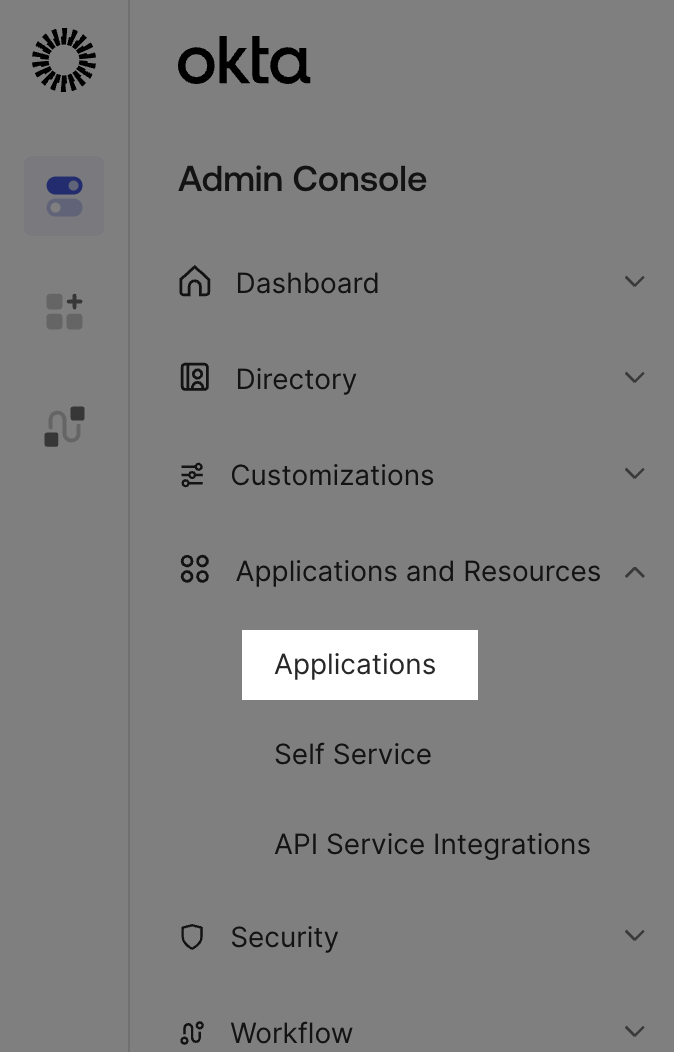
1. In the navigation menu of the Okta Admin Console, click **Applications**.
   ![Navigating to applications in the Okta Admin Console](https://docs.coveo.com/en/assets/images/manage-an-organization/sso-okta-apps.png)

1. Depending on your needs, determine whether you'll [use the pre-configured application](https://docs.coveo.com/en/1602.md#coveo-pre-configured-application) or [create an application manually](https://docs.coveo.com/en/1602.md#manual-application-configuration):

   [cols="~,^~,^~"]
   |===
   | Application | Supports [assertion encryption](https://docs.coveo.com/en/1979.md#assertion-encryption) | Supports [importing groups into Coveo](#about-importing-okta-groups-into-coveo)

| [Pre-configured](https://docs.coveo.com/en/1602.md#coveo-pre-configured-application)
|[No]
|[Yes] [_See below_](#about-importing-okta-groups-into-coveo)

| [Manually created](https://docs.coveo.com/en/1602.md#manual-application-configuration)
| [Yes]
| [Yes]

| === | Name | Name format | Value |
|---|---|---|---|
| `user.email` | Unspecified | `user.email` |  |

1. Optionally, click **Add Another** to add more attribute statements.
They all should be in `Unspecified` format.
See [Okta Expression Language](https://developer.okta.com/reference/okta_expression_language/) for reference.
+
**Example**

You could choose to add the following rules:

| Name | Name format | Value |
|---|---|---|
| `user.firstName` | Unspecified | `user.firstName` |
| `user.lastName` | Unspecified | `user.lastName` |

1. Click **Save**.

1. [Assign your application to users and groups](#assign-your-application-to-users-and-groups).

## Assign your application to users and groups

Once you've created an Okta application and configured it so that it passes user authentication to Coveo, you must [assign it to your Okta users](#assign-application-to-users) and/or [groups](#assign-application-to-groups).

Assigning your app to groups is especially useful, as it allows you to [add Okta users in bulk to Coveo groups](#about-importing-okta-groups-into-coveo).

### Assign application to users

Assign your application to the Okta users you want to allow to log in to Coveo using Okta SSO, including yourself:

1. On the **Applications** Okta page, click **Assign Users to App**.

1. On the **Assign Applications** page:

 .. Under **Applications**, select your Coveo application.

 .. Under **People**, select the users you want to allow to log in to Coveo using Okta SSO.

 .. Click **Next**.

 .. Review your application assignments, and then click **Confirm Assignments**.

1. Optionally, [assign your application to Okta groups](#assign-application-to-groups).

1. [Prepare to configure Coveo](#prepare-to-configure-coveo).

Alternatively, see [Assign Applications to users](https://help.okta.com/en/prod/Content/Topics/users-groups-profiles/usgp-assign-apps.htm).

### Assign application to groups

Assigning your app to groups is especially useful, as it allows you to [import your Okta groups into Coveo](#about-importing-okta-groups-into-coveo) and add Okta users to Coveo groups in bulk rather than individually.

1. In Okta, add yourself to all groups you're planning to import into Coveo.
This is necessary because Coveo will only show you the Okta groups of which you're a member.
As an administrator, you may therefore want to be a member of all groups.

1. On the **Applications** Okta page, click your Coveo application.

1. On the **Assignments** tab, click the **Assign** dropdown menu, and then click **Assign to Groups**.

1. In the dialog that appears, click **Assign** for each group you want to import into Coveo, and then click **Done**.

1. Edit your Okta application to enter an attribute statement regarding the user groups to import:

   .If using a pre-configured app
   <details><summary>Details</summary>

1. On your Okta application page, select the **Sign On** tab.

1. Next to **Settings**, click **Edit**.

1. In the **user.groups** box, select an operator and enter a value.

   > **Note**
   >
   > Pre-configured applications support entering only one expression.
   > If you need to enter more than one expression, [create an application manually](#manual-application-configuration) instead.

   For example:

    * `Matches .*` imports all Okta groups into Coveo.

    * `Contains Department` imports the `Human Resources Department`, `Engineering Department`, and `Sales Department` groups into Coveo, but not the `Engineering Interns` and `Okta Administrators` groups.

    * `Equals Support Agents` imports only the `Support Agents` group.
Other groups aren't imported.

</details>
+
**If using a manually created app**
<details><summary>Details</summary>

1. On your Okta application page, select the **Sign On** tab.

1. Under **Attribute statements**, click **Show legacy configuration**.

1. Click **Edit**.

1. Under **Group attribute statements**, enter at least one attribute statement to specify which Okta groups can be imported Coveo.
The name format must remain `Unspecified`.
+
**Examples**

* The following statement imports all Okta groups into Coveo:

  |===
  | Name | Name format | Filter

| `user.groups`
| Unspecified
| Matches regex `.*`

| === | Name | Name format | Filter |
|---|---|---|---|
| `user.groups` | Unspecified | Contains `Department` |  |

* The following statements imports the `Support Agents`, `Software Developers`, and `User Interface Designers` groups into Coveo.
Other groups aren't imported.
+

| Name | Name format | Filter |
|---|---|---|
| `user.groups` | Unspecified | Equals `Support Agents` |
| `user.groups` | Unspecified | Equals `Software Developers` |
| `user.groups` | Unspecified | Starts with `User` |

</details>
1. Click **Save**.

1. Optionally, [assign your application to individual Okta users](#assign-application-to-users).

1. [Prepare to configure Coveo](#prepare-to-configure-coveo).

## Prepare to configure Coveo

Once you've [configured your Okta application](#configure-okta) and [assigned it to users and/or groups](#assign-your-application-to-users-and-groups), you must retrieve Okta's URIs and public certificate.
This information will allow you to configure Coveo and enable federation with Okta.

1. On the **Applications** Okta page, click your [Coveo application](#configure-okta).

1. Select the **Sign On** tab.

1. Under **Sign on methods**, in the **SAML 2.0** box, click **More details** to reveal the data required to configure Coveo.

1. [Configure Coveo](#configure-coveo).

## Configure Coveo

Once you've configured your identity provider to provide Coveo with user authentication data, you must configure Coveo to trust your identity provider and accept to rely on it for user authentication.

1. With the [data required to fill the Coveo configuration form](#prepare-to-configure-coveo) in hand, access the **Settings** page:

   1. [Log in to Coveo](https://platform.cloud.coveo.com/login) ([platform-ca](https://platform-ca.cloud.coveo.com/login) | [platform-eu](https://platform-eu.cloud.coveo.com/login) | [platform-au](https://platform-au.cloud.coveo.com/login)) as a [member](https://docs.coveo.com/en/2869.md) of a [group](https://docs.coveo.com/en/2867.md) with the [required privileges](https://docs.coveo.com/en/1562.md#required-privileges) to manage settings in the target [Coveo organization](https://docs.coveo.com/en/185.md).

   1. On the **Settings** page, select the **Organization** tab, and then select the [**Single sign-on**](https://platform.cloud.coveo.com/admin/#/orgid/settings/organization/sso) ([platform-ca](https://platform-ca.cloud.coveo.com/admin/#/orgid/settings/organization/sso) | [platform-eu](https://platform-eu.cloud.coveo.com/admin/#/orgid/settings/organization/sso) | [platform-au](https://platform-au.cloud.coveo.com/admin/#/orgid/settings/organization/sso)) subtab.

1. In the **Single sign-on** subtab, in the **Identity provider name** box, enter the identity provider name as you want it to appear on your Coveo organization [login page](https://docs.coveo.com/en/1697.md).

1. In the **Single sign-on URL** box, enter the URL where Coveo must send an authentication request.
In Okta, you can [find it under **Sign on URL**](#prepare-to-configure-coveo).

1. In the **Identity provider issuer URI** box, enter the identity provider issuer unique URI.
In Okta, you can [find it under **Issuer**](#prepare-to-configure-coveo).

1. Using one of the following methods, provide Coveo with the identity provider's Base64 public certificate to validate the identity provider signature:

  * Paste the certificate in the **X.509 public certificate** box.

  * If you saved the certificate on your computer, click **Upload** to browse your files and upload the certificate.

1. Click **Add**.

1. Optionally, [encrypt Okta assertions](#encrypt-okta-assertions).

1. [Test your configuration](#test-your-configuration).

## Encrypt Okta assertions

[Assertion encryption](https://docs.coveo.com/en/1979.md#assertion-encryption) is optional.
To encrypt Okta assertions, retrieve the Coveo public certificate and import it into your Okta configuration:

1. On the **Settings** page, on the [**Single sign-on**](https://platform.cloud.coveo.com/admin/#/orgid/settings/organization/sso) ([platform-ca](https://platform-ca.cloud.coveo.com/admin/#/orgid/settings/organization/sso) | [platform-eu](https://platform-eu.cloud.coveo.com/admin/#/orgid/settings/organization/sso) | [platform-au](https://platform-au.cloud.coveo.com/admin/#/orgid/settings/organization/sso)) tab, download Coveo's certificate.

1. Back on your Okta application page, select the **General** tab.

1. In the **SAML Settings** box, click **Edit**.

1. Click **Next**.

1. Under **General**, click **Show Advanced Settings**.

1. In the **Assertion Encryption** dropdown menu, select **Encrypted**.

1. Next to **Encryption Certificate**, click **Browse files**, and the select the Coveo certificate.

1. Click **Next**, and then complete the wizard.

1. [Test your configuration](#test-your-configuration).

## Test your configuration

Once you've completed the SSO configuration, test the login process to ensure it works as expected.
To do so, you'll need to add your SSO identity as a member of your Coveo organization.
You can't use the account you've used to configure SSO, as it's associated with a different identity provider.
See [Login options](https://docs.coveo.com/en/1697.md#login-options) and [Multiple accounts](https://docs.coveo.com/en/1697.md#multiple-accounts) for details.

1. [Add your email address as an organization member](https://docs.coveo.com/en/1821.md).
In the **Add a Member** dialog, under **Provider**, ensure to select **Single sign-on**.

1. [Log out of the Coveo Administration Console](https://docs.coveo.com/en/1841.md#user-menu), and then [log back in using the SSO option and your identity provider account](https://docs.coveo.com/en/1697.md#logging-in-with-sso).
By doing so, you ensure Coveo and your identity provider work together properly.

+
> **Important**
>
> We strongly recommend that you don't delete the account with which you first logged in to the Administration Console and implemented SAML SSO.
> This original account is a "backdoor" that prevents you from being locked out if the SAML SSO doesn't work as expected.
> At any time, you can log in with your original, non-SSO identity provider, and then edit the Coveo configuration.
> For details on how accounts belonging to the same individual are separated, see [Multiple Accounts](https://docs.coveo.com/en/1697.md#multiple-accounts).
>
> Alternatively, if you must delete your original account, you can also create another non-SSO administrator account with the [required privileges](https://docs.coveo.com/en/1562.md#required-privileges) beforehand.
> [Logging in via email](https://docs.coveo.com/en/1697.md#logging-in-with-email) is also an alternative.

1. [Invite SSO users or user groups](#invite-sso-users-or-user-groups).

## Invite SSO users or user groups

Once you've verified that your SSO configuration works, invite SSO users to join your Coveo organization.

> **Important**
>
> Once your SSO is active, promptly add your users to the organization as SSO users so they can log in successfully.
> When an organization has an SSO configured, users accessing a hosted search page of this organization are directed by default to the [SSO login page](https://docs.coveo.com/en/1697.md).
> If a user hasn't been added to Coveo as an SSO user, they can authenticate with their identity provider, but they won't be able to access the hosted search page because no corresponding Coveo SSO user exists.

Add users to your Coveo organization by using either or both of these methods:

* [Adding them one by one](https://docs.coveo.com/en/1980.md#add-specific-members-to-a-group) through the [**Members**](https://platform.cloud.coveo.com/admin/#/orgid/organization/members/) ([platform-ca](https://platform-ca.cloud.coveo.com/admin/#/orgid/organization/members/) | [platform-eu](https://platform-eu.cloud.coveo.com/admin/#/orgid/organization/members/) | [platform-au](https://platform-au.cloud.coveo.com/admin/#/orgid/organization/members/)) page.

* If you've decided to import SSO groups into Coveo, you can [add a group of SSO users to a Coveo group](https://docs.coveo.com/en/1980.md#import-members).

## Configure SSO in another organization

If you have multiple Coveo organizations, such as a production organization and a [sandbox organization](https://docs.coveo.com/en/2959.md), you must use the same SSO settings for all organizations.
Users will then use the same SSO credentials to log in, regardless of the organization they are accessing.

Follow these steps to configure SSO in additional organizations:

1. Ensure that the user identity you'll use to configure SSO:

   --
  * Is a [member](https://docs.coveo.com/en/2869.md) of all [organizations](https://docs.coveo.com/en/185.md) where the SSO configuration will be used, including the original organization where SSO is already configured.
If it's not already a member, this user identity must be [invited](https://docs.coveo.com/en/1821.md#add-members) to the organizations and [accept the invitations](https://docs.coveo.com/en/1697.md#after-login).
  * Has the [privilege](https://docs.coveo.com/en/228.md) to edit SSO settings (**Edit** on the [**Single sign-on identity provider** domain](https://docs.coveo.com/en/1707.md#single-sign-on-identity-provider-domain)) in each of these organizations.
--

1. Using this identity, log in to the organization where you want to configure SSO.

1. In the [**Single sign-on**](https://platform.cloud.coveo.com/admin/#/orgid/settings/organization/sso) ([platform-ca](https://platform-ca.cloud.coveo.com/admin/#/orgid/settings/organization/sso) | [platform-eu](https://platform-eu.cloud.coveo.com/admin/#/orgid/settings/organization/sso) | [platform-au](https://platform-au.cloud.coveo.com/admin/#/orgid/settings/organization/sso)) tab of the **Settings** page, delete any existing SSO configuration.
Save your change.
This will also permanently delete the associated SSO members from your Coveo organization.

1. Copy the SSO settings from the first organization to the other.
The SSO settings provided to Coveo must be identical across all organizations, including the identity provider name.
+
> **Tip**
>
> Open the organization where SSO was originally configured in a private browser window.
> This will let you copy and paste from one organization to the other without logging in and out to switch between them.

1. Follow the remainder of the deployment process above, starting at the assertion encryption step, for each organization where you copied the SSO settings.

## Required privileges

The following table indicates the [privileges](https://docs.coveo.com/en/228.md) required to configure SSO on the [**Single sign-on**](https://platform.cloud.coveo.com/admin/#/orgid/settings/organization/sso) ([platform-ca](https://platform-ca.cloud.coveo.com/admin/#/orgid/settings/organization/sso) | [platform-eu](https://platform-eu.cloud.coveo.com/admin/#/orgid/settings/organization/sso) | [platform-au](https://platform-au.cloud.coveo.com/admin/#/orgid/settings/organization/sso)) page (see [Manage privileges](https://docs.coveo.com/en/3151.md) and [Privilege reference](https://docs.coveo.com/en/1707.md)).

| Action | Service | Domain | Required access level |
|---|---|---|---|
| View SSO configuration | Organization | Organization | View |
| View SSO configuration | Organization | Single sign-on identity provider | View |
| Edit SSO configuration | Organization | Organization | View |
| Edit SSO configuration | Organization | Single sign-on identity provider | Edit |

> **Note**
>
> Granting the **Edit** access level on a domain also implicitly grants **View** on that domain.

